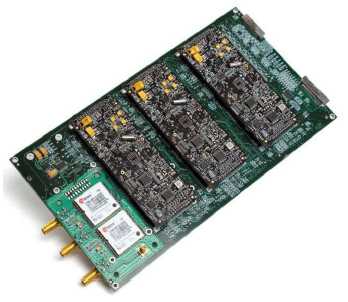
MicroPilot 21283X
How long before this becomes a standard required by authorities??
The MP21283X, MicroPilot’s triple-redundancy (3X) autopilot, is now available. Although 3X technology is established within the aviation industry, 3X autopilots are a new addition to unmanned aerial vehicles (UAVs). The MP21283x contains three robust autopilots to overcome a multitude of hardware failures. If any one of the three autopilots should fail, the remaining two take over. An additional mechanism oversees these three systems.

Comments
Not sure a dozencopter would be needed but I will bet there will be some requirement for redundant power for commercial use. I flew full scale helicopters for a bit and am glad I had two engines on a few occasions. And it's not a new situation in commercial aviation. Depending on what FAR part you are building towards will drive some of the safety factors required for certain parts - larger safety for rotational forces, redundancy for flight critical avionics, etc. I think it will be the same for UAS's in the commercial market. At the smaller end with just flight stabilization for work like line of site AP I hope the requirements are sensible. Even if they do not require at least level flight with one motor out I think I will still build that way so I do not waste a good camera.
Anyway it's all speculation on my part as to what the FAA will decide, and hopefully we can all afford to be compliant after the dust settles.
"Single motor failure on a quad and bye bye!"
Riiight. Clearly, it would be irresponsible to allow less than a dozencopter for any commercial application.
One thing is interesting.
How do they handle mission porgramming?
Say you connect the autopilot to the USB. You type "send me the IMU status'. Then what. Or imagine downloading logs.
It is easy to multiplex output: put a median on it and it's done. But then you watch the logs of the 3 perfectly performing systems. See what? One is winning 30% of the time, another 50%, another 20%. Have fun watching all those little jumping variables.
Or uploading a mission using telemetry. Who tells the new request has been sucessful: when most of the AP got their target? Reasonnable proposal.
Imagine:
You upload new waypoint:
2 autopilots accepted, 1 refused.
Downlink report operation failed - cool.
But now 2 of 3 APs are following a new route, and median wins using their opinion.
So the autopilot IS following a new route. Yet the update has failed.
You see? You need full commit-or-rollback on ALL units on ALL logic. Including log delete etc.
How costly is that?
Imagine you upload all waypoint (say 1024).
3rd autopilot messes up at 1000th waypoint. You have 1024+1024+1000 to roll back, in realtime, and while doing so, the aircraft has to follow the original route.
Now imagine that one of the autopilots was doing his rollback, but the already degrading power supply has finally triggered its brown-out reset. The rollback is partially complete and has to continue upon reboot.
Coby means on a Quadcopter. He has the nicest carbon fiber frame on the planet!!!
Single motor failure on a quad and bye bye!
"Of course having three IMU's doesn't do much good if you only have four motors."
Not sure how to interpret this...
Of course I understand redundancy is probably a requirement lobbied by somebody, but unless it is based on statistics, you could as well request cars to have 5 wheels for extra safety. My fear is, based on common sense and knowledge how one would evaluate the robustness, that putting 3 identical systems in parallel is only able to eliminate soldering issues, while the complexity is in the software.
The weakest link is, that all the 3 autopilots from the same make and the same engineering group, is VERY LIKELY to fail all the three for the same reason (consider GPS firmware lockup or unexpected premature freezing of a given batch of baro sensor).
A selection of ardupilot+unav+atto+flexipilot woudl be cheaper and more resistant, but then, it becomes nearly impossible to tell which is right if all have different control methods, different goals and safety margin.
If a well managed company wants to build a good redundant system, they make 2 engineering teams and if possible they are asked to occupy different company buildings at least, if not to relocate to another city (in order to reduce cross-team communication, besides defining digital control+arbitration protocol).
The solution as it is, is mostly marketing, it will overload power and fail miserably for the same 'millennium bug' should it reappear in a different form.
One more thing the product is at least one year old if I remember well.
The RC boys have been flying with redundant systems for years. Including servos. The wings? Maybe not but that structural and we are talking flight control systems.
Having an Autopilot backup may come down to simple finances. Imagine you have a research UAV with a $10,000 sensor on board. For the price of an additional APM and IMU, taking that single point of failure may well be worth it.
@ Mike
I see your point, but I've only been considering system outage/failure scenarios really. These seem to be the most likely type of failure.
Regards
D
i see no problem - write a mockup for those not online/active and you are done.
:)
nails the problem down to who has access to the hw.
-
1
-
2
-
3
of 3 Next